AI Acceptable Use Policy: Free Template And How To Write One
Dave Roberts
Founder and CEO - ReVerb
27.09.2026
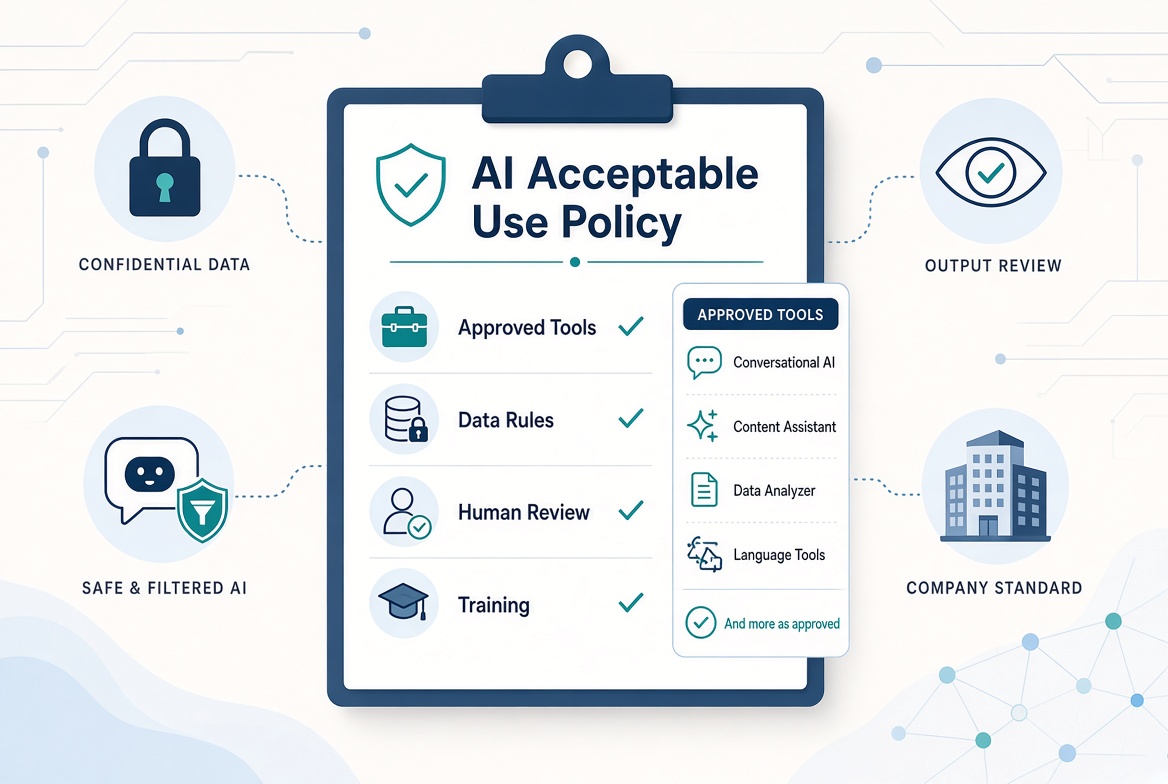
Short answer: An AI acceptable use policy is a short internal document that tells employees which AI tools they may use, what data they may put into them, how AI output must be checked, and what happens when the rules are broken. You can copy the free AI policy template below, adapt the bracketed sections to your company, and have a working first version live within a week.
Most companies already have an AI policy. It just is not written down. Employees are pasting emails, spreadsheets, code and customer notes into chatbots every day, and in the absence of clear rules each person is making their own call about what is safe. A written AI acceptable use policy replaces those private judgment calls with one shared standard, gives managers something to point to, and gives the company a defensible position if something goes wrong.
This guide covers what an AI usage policy is, what it should include, a complete template you can copy, a seven-step process for writing your own, three AI policy examples at different risk levels, and how to enforce the rules without pushing AI use underground.
An AI acceptable use policy (often shortened to AI AUP, and also called an AI usage policy, a generative AI policy or a company AI policy) is a set of rules that governs how employees, contractors and other staff use artificial intelligence tools at work. It sits alongside your existing IT acceptable use policy, information security policy and data protection policy, and borrows their structure: scope, permitted use, prohibited use, responsibilities and consequences.
What makes an AI policy different from a general IT policy is that AI tools do two things other software does not. They take whatever you type in and send it to a third party model provider, and they produce output that looks authoritative but can be wrong, biased or copied from someone else. A good AI acceptable use policy is built around controlling both of those: what goes in, and what comes out.
It is also worth separating an AI acceptable use policy from an AI governance policy. The acceptable use policy is written for every employee and answers the question “what am I allowed to do?” An AI governance policy is written for leadership, legal and technical teams and covers how the company selects, builds, tests and monitors AI systems. Smaller companies often combine the two. Larger ones keep the acceptable use policy short and readable and put the governance detail in a separate document.
Aspect
AI Acceptable Use Policy
AI Governance Policy
Audience
Every employee and contractor
Leadership, legal, security, data and engineering teams
Main question
What am I allowed to do with AI?
How does the company choose, build and oversee AI?
Typical length
2 to 5 pages
10 pages or more
Covers
Approved tools, data rules, output review, disclosure, consequences
Risk classification, vendor assessment, model testing, monitoring, accountability
Updated
Every 6 to 12 months, or when tools change
Annually, or when regulation changes
Why Your Company Needs An AI Policy In 2026
Three pressures have turned an AI policy from a nice-to-have into a basic control.
Shadow AI Is Already Happening
Shadow AI is the use of AI tools without approval from IT or security, and it is the default state in any company without a policy. Employees sign up for chatbots, note takers, writing assistants and coding agents on personal accounts because the tools are genuinely useful. Every one of those accounts is a place where company data can end up outside your control, often under terms that allow the provider to retain it or use it for training. You cannot fix shadow AI with a policy alone, but you cannot fix it at all without one, because until the rules are written down nobody is actually breaking them.
Regulation Now Expects It
The EU AI Act has required organizations that deploy AI systems to take measures to ensure a sufficient level of AI literacy among their staff since 2 February 2025, under Article 4. A written policy backed by training is the most straightforward way to show that. Frameworks such as the NIST AI Risk Management Framework and ISO/IEC 42001, the international standard for AI management systems, also treat documented policy as a foundation. Outside AI-specific law, existing privacy rules such as GDPR and sector rules in healthcare and finance already apply to any personal or regulated data an employee pastes into a chatbot.
Customers And Insurers Are Asking
Security questionnaires from enterprise customers now routinely ask whether you have an AI usage policy, which tools are approved, and whether customer data is ever entered into AI systems. Cyber insurers are starting to ask similar questions. “We are working on it” is a weaker answer every quarter.
What Should An AI Policy Include?
Every AI acceptable use policy needs the same core sections, whatever the size of the company. The table below lists them with the question each one answers.
Section
What It Answers
Purpose and scope
Why the policy exists and who and what it covers (employees, contractors, company devices, personal devices used for work)
Definitions
What counts as an AI tool, including AI features inside approved software and AI agents
Approved tools
Which AI tools and accounts are sanctioned, and for which uses
Requesting a new tool
How an employee gets a tool reviewed and who approves it
Data classification rules
Which categories of data may and may not be entered into AI tools
Prohibited uses
What is never allowed, regardless of tool
Output review and accuracy
Who is responsible for checking AI output before it is used
Disclosure and transparency
When customers, colleagues or the public must be told AI was used
Intellectual property
Who owns AI-assisted work and how to avoid infringing others
AI agents and automation
Rules for tools that act on their own, connect to systems or run code
Monitoring
That AI use on company systems may be monitored, and why
Training
What training staff must complete and how often
Reporting and incidents
How to report a mistake, a leak or a suspicious tool
Consequences
What happens when the policy is breached
Ownership and review
Who owns the policy and when it will be reviewed
The single most important section is the data classification rule. If an employee remembers only one thing from your AI policy, it should be which kinds of information must never go into an AI tool that the company has not approved.
Free AI Acceptable Use Policy Template
Copy the AI policy template below into your own document and replace everything in square brackets. It is written to be read by every employee in under ten minutes, so resist the urge to make it longer. Detail that only the security or legal team needs belongs in a separate governance document or procedure.
This sample AI policy is a starting point, not legal advice. Have it reviewed by your legal or compliance adviser before you adopt it, particularly if you operate in a regulated industry or in more than one country.
1. Purpose
[Company Name] encourages the responsible use of artificial intelligence to help us work faster and better. This policy sets out how AI tools may be used at [Company Name] so that we protect our customers, our employees, our data and our reputation while getting real value from AI.
2. Scope
This policy applies to all employees, contractors, interns and temporary staff of [Company Name] (together, “staff”). It covers any use of AI tools for [Company Name] work, whether on company devices, personal devices or any other system, and whether the tool is free or paid.
3. Definitions
AI tool means any software that uses artificial intelligence to generate, summarize, translate, classify or analyze content, including chatbots, writing assistants, image and video generators, meeting note takers, coding assistants, and AI features built into other software.
AI agent means an AI tool that can take actions on its own, such as sending messages, editing files, calling other systems or running code.
Approved AI tool means a tool and account type listed in the Approved AI Tools register maintained by [IT / Security team].
Confidential information has the meaning given in [Company Name]’s [Information Security Policy / Data Classification Policy].
4. Approved AI Tools
Staff may use only the AI tools listed in the Approved AI Tools register, and only through company-provided accounts where the register says so. The register is available at [location] and lists each tool, the account type that must be used, and the data categories permitted in it. Using a personal account for an approved tool (for example, a personal chatbot account instead of the company’s enterprise workspace) is not permitted for [Company Name] work.
5. Requesting A New AI Tool
To request a new AI tool, submit [form / ticket] to [IT / Security team] describing the tool, the business need and the data it would handle. [IT / Security team] will aim to respond within [10] working days. Staff must not use a tool for [Company Name] work until it has been approved. This includes browser extensions, plugins and AI features that are switched on inside software we already use.
6. Data Rules
Staff must follow these rules for any information entered into, uploaded to or connected to an AI tool:
Data Category
Approved AI Tools
Unapproved AI Tools
Public information
Permitted
Permitted
Internal information (not public, low sensitivity)
Permitted
Not permitted
Confidential information (customer data, financials, contracts, source code, strategy)
Permitted only where the register allows it
Never permitted
Personal data about customers, staff or others
Permitted only where the register allows it and a lawful basis exists
Never permitted
Restricted data (passwords, credentials, keys, payment card data, health records, [other regulated data])
Never permitted
Never permitted
If you are not sure which category information falls into, treat it as confidential and ask your HR manager.
7. Prohibited Uses
Regardless of the tool, staff must not use AI to:
make or materially influence final decisions about hiring, firing, promotion, pay, credit, or access to services without human review and the approval of [HR / Legal];
create content that is unlawful, discriminatory, harassing, deceptive or defamatory;
impersonate a real person, or create realistic images, audio or video of a real person without their consent;
produce advice presented as professional legal, medical or financial advice to customers without review by a qualified person;
bypass, disable or evade [Company Name]’s security controls, including any monitoring of AI use;
infringe the intellectual property or confidentiality rights of others, including by uploading third-party material the company does not have the right to use
8. Accuracy And Human Review
AI output can be wrong, out of date, biased or invented. The person who uses AI output is responsible for it as if they had written it themselves. Staff must review and verify AI output before it is sent to a customer, published, used in a decision, or merged into production code. Facts, figures, citations, legal references and code must be checked against a reliable source.
9. Disclosure
Staff must disclose AI use when [a customer contract requires it / content is published under a person’s name / AI generates images or media that could be mistaken for real / a customer is interacting with an AI system rather than a person]. When in doubt, disclose.
10. Intellectual Property
Work created by staff with the help of AI tools in the course of their employment belongs to [Company Name] to the extent permitted by law. Staff should be aware that purely AI-generated material may not be protected by copyright in some countries, and that AI output can reproduce third-party material. Do not use AI to recreate a competitor’s copyrighted content, and run [code scanning / plagiarism checks] where the register requires it.
11. AI Agents And Automation
AI agents and automations that can act on [Company Name] systems (for example, by reading or sending email, editing records, connecting to internal tools or running code) require approval from [IT / Security team] before use, even if the underlying AI tool is approved. Each approved agent must have a named owner who is responsible for its permissions and behavior.
12. Monitoring
[Company Name] may monitor the use of AI tools on company systems and networks to protect its data and to enforce this policy, in line with applicable law and [Company Name]’s [Monitoring / Privacy Notice for Staff].
13. Training
All staff must complete [Company Name]’s AI awareness training within [30] days of joining and [annually] after that. Staff in roles that use AI heavily may be required to complete additional training.
14. Reporting Incidents
If you think confidential or personal data has been entered into an unapproved AI tool, or an AI tool has behaved unexpectedly, report it immediately to [contact / channel]. Early reporting is always treated more favorably than a problem that is discovered later.
15. Consequences
Breaches of this policy may lead to loss of access to AI tools and to disciplinary action up to and including dismissal, in line with [Company Name]’s [Disciplinary Policy]. Breaches by contractors may lead to termination of their engagement.
16. Ownership And Review
This policy is owned by [role]. It will be reviewed at least every [12] months, and sooner if [Company Name] adopts significant new AI tools or relevant law changes. Last reviewed: [date]. Version: [number].
How To Write An AI Acceptable Use Policy In 7 Steps
A template gets you a document. These steps get you a policy people actually follow.
Step 1: Find Out What AI Is Already In Use
Before you write a word, find out which AI tools your staff already use and what they use them for. An anonymous survey works for a small company. Larger organizations can pull data from their identity provider, expense reports and security tools, or use dedicated shadow AI detection software. You will almost certainly find more tools than you expected, and the list will tell you which approved alternatives you need to provide.
Step 2: Pick An Owner And A Small Working Group
One person needs to own the policy. In most companies that is the head of IT or security, the data protection officer, or the general counsel. Give them a small group that includes someone from legal or compliance, HR, and one or two heavy AI users from the business. Leaving out the business users is how you end up with a policy nobody can follow.
Step 3: Decide Your Risk Posture
Decide whether you are starting restrictive, balanced or permissive (the examples section below compares the three). This one decision shapes every other section of the policy, so settle it with leadership before drafting.
Step 4: Build The Approved Tools Register
Choose the tools you will officially support and, wherever possible, buy the business or enterprise version. Business tiers of the major AI tools typically offer contractual commitments on data retention and training, admin controls and single sign-on, which personal accounts do not. Record each tool, its account type and the data categories allowed in it. Keep the register as a separate, living document so you can update it without reissuing the whole policy.
Step 5: Write The Data Rules First
Map your AI data rules onto the data classification scheme you already use. If you do not have one, the five categories in the template (public, internal, confidential, personal and restricted) are a reasonable start. Then draft the rest of the policy around those rules.
Step 6: Review, Approve And Launch
Have legal and HR review the draft, get sign-off from leadership, and launch it with a short announcement that explains why the policy exists and which approved tools are available. Pair the launch with training. A policy that arrives with a useful approved tool gets a very different reception from one that arrives as a list of bans.
Step 7: Review It Every Six To Twelve Months
AI tools change faster than almost any other category of software. Put a review date in the policy and keep it. At each review, check the approved tools register, any incidents, new regulation, and the questions staff keep asking, because repeated questions are a sign a section is unclear.
AI Policy Examples: Three Approaches
There is no single right level of restriction. These three AI policy examples show how the same sections read under different risk postures.
Factor
Restrictive
Balanced
Permissive
Best for
Healthcare, finance, defense, legal, government
Most businesses
Startups, agencies, marketing teams
Approved tools
One or two enterprise tools only
A short register of business-tier tools
Most mainstream tools on business accounts
New tool requests
Formal security and legal review
Lightweight review by IT
Self-service within listed categories
Confidential data
Never, in any tool
Only in approved enterprise tools
In approved tools with sensible judgment
AI agents
Not permitted
Permitted with approval and a named owner
Permitted within set permissions
Monitoring
Active monitoring and blocking
Monitoring with coaching
Periodic review
Main risk
Staff route around it with personal accounts
Needs steady upkeep of the register
Data leakage and unchecked output
Most companies should start balanced. A restrictive policy with no useful approved tools tends to create more shadow AI rather than less, because people keep using the tools that help them and simply stop telling you.
How To Enforce An AI Policy Without Driving AI Underground
The goal of enforcement is safe AI use, not zero AI use. A few practices make the difference.
Provide the approved alternative first. Ban a personal chatbot without offering a company version and usage simply moves to phones and home laptops.
Coach before you block. Tools that warn a user in the moment (“this looks like customer data, use the company workspace instead”) change behavior more than silent blocking.
Make requesting a tool fast. If approval takes two months, people will not wait. A published turnaround target keeps requests coming through the front door.
Reward reporting. Say plainly in the policy that early self-reporting of a mistake is treated favorably. You want to hear about leaks from staff, not from customers.
Measure it. Security platforms and dedicated shadow AI detection tools can show which AI apps are in use and what data is flowing into them, which tells you whether the policy is working and where the register has gaps.
Staff use personal accounts where you have no visibility
Approve at least one business-tier tool and set data rules
Naming tools in the policy itself
The policy is out of date within months
Keep tools in a separate register the policy points to
Forgetting embedded AI
AI features switch on inside software you already approved
Define AI tool to include AI features in other software
Ignoring AI agents
Agents act without a human typing anything
Require approval and a named owner for each agent
Writing for lawyers only
Nobody reads a 20-page policy
Keep the AUP short and move detail to governance documents
No training
Staff do not know the rules exist
Launch with training and repeat it annually
No review date
The policy quietly goes stale
Set a review cycle and put the date in the document
FAQ
What is the difference between an AI acceptable use policy and an AI usage policy?
In practice they are the same thing. “AI acceptable use policy”, “AI usage policy”, “AI use policy” and “company AI policy” are all used for the employee-facing rules on how AI tools may be used at work.
Do small businesses need an AI policy?
Yes. A small business has less margin for a data leak or a public mistake, not more. A one or two page policy covering approved tools, data rules and output review is enough to start, and the template above can be cut down to fit.
Is an AI acceptable use policy a legal requirement?
No law in most countries requires a document with that exact name. However, the EU AI Act requires organizations deploying AI to ensure sufficient AI literacy among staff, privacy law governs any personal data entered into AI tools, and customer contracts increasingly ask about AI use. A written policy is the simplest way to meet all three. Take legal advice for your own jurisdiction.
Can employees use ChatGPT at work?
That depends on your policy. Many companies allow ChatGPT or similar chatbots only through a company-managed business or enterprise account, and prohibit entering confidential or personal data into personal accounts. Your approved tools register should say exactly which accounts are allowed.
Who should own the AI policy?
Usually the head of IT or security, the data protection officer or the general counsel, supported by a small working group from legal, HR and the business. What matters most is that one named person is accountable for keeping it current.
How long should an AI acceptable use policy be?
Two to five pages for the policy itself. If yours is much longer, move technical and procedural detail into separate governance documents so employees can read the rules that apply to them in one sitting.
How often should an AI policy be updated?
At least every twelve months, and every six months is better while the tools are changing this quickly. Update it sooner when you adopt a significant new tool, have an incident, or relevant law changes.
Should the policy cover AI features inside software we already use?
Yes. Many shadow AI cases involve AI features that vendors switch on inside approved software. Define “AI tool” broadly enough to include them, and require that new AI features go through the same review as a new tool.
What is a generative AI policy template?
A generative AI policy template is a ready-made AI usage policy focused on tools that create text, images, code or audio. The template in this guide is a generative AI policy template that also covers AI agents and AI features embedded in other software.
The Short Version
An AI acceptable use policy tells staff which AI tools they may use, what data can go into them, how output must be checked and what happens if the rules are broken.
The data rules are the most important section: spell out which categories of information may never go into an unapproved tool.
Keep approved tools in a separate register so the policy does not go stale.
Start with a balanced posture and provide approved business-tier tools, or AI use will move to personal accounts.
Cover AI agents and AI features inside existing software, not just chatbots.
Launch with training, coach before you block, and review the policy every six to twelve months.