For a PHP security audit, the strongest picks are Paragon Initiative Enterprises, SektionEins and Valorin Security.
Paragon Initiative Enterprises is a PHP specialist whose published advisories cover PHP object injection in Laravel and cryptography flaws in Zend Framework and Joomla, and it sends patches or pull requests along with its audit report. SektionEins, in Bonn, has tested web applications since 2007, maintains PHP security tooling such as the PHP Secure Configuration Checker, and runs a four-stage source code analysis mapped to the OWASP Web Security Testing Guide. Valorin Security is the practice of Laravel security specialist Stephen Rees-Carter, who starts every engagement by reading your code and then uses those findings to steer a penetration test of a staging environment.
This list is for CTOs, engineering leads, agencies and plugin vendors who need someone to read their PHP code for security flaws, whether that is a custom PHP application, a Laravel or Symfony product, a WordPress plugin or theme, or a Magento store. To be included, a firm had to sell a named security audit or secure code review service, and preference went to firms whose own pages name PHP or a PHP framework in that offering. Every firm was checked against its own service pages, and only details those pages state are included here.
Paragon Initiative Enterprises is a Florida technology company based in Naples that sells independent source code audits with an application security focus, and PHP is the center of that work. Its audit page lists the classic web flaws it hunts for, including SQL injection, file inclusion, cross-site scripting, directory traversal and broken access control, along with PHP-specific and harder-to-spot issues such as PHP object injection, weak random number generation, cryptographic side channels and insecure password storage.
The process is simple. You share the latest commit through temporary Git access or an encrypted archive, Paragon audits it over an agreed period and delivers a report. If it finds problems, it works with your team on fixes, often by sending patches or pull requests, and then issues a revised report showing what was resolved. The firm says it does not rely on an automated scanner and a rubber stamp, preferring a manual review that reduces false positives.
Its published advisories are a useful track record for a PHP security code review buyer: a PHP object injection issue in Laravel, a padding oracle in Zend Framework’s RSA class, cryptography flaws in Joomla’s JCrypt library, and object injection in Simple Machines Forum and AnchorCMS.
Best for: Teams with custom PHP applications, especially ones that handle cryptography, authentication or payments, that want fixes delivered as code rather than only a findings list.
SektionEins is a Bonn, Germany security firm that has tested web and mobile applications since 2007 and has deep roots in PHP security. Its site documents the return of Suhosin, the PHP hardening extension, and a 2026 update of PCC, its PHP Secure Configuration Checker, with new checks for PHP 8.x. PHP sits on its list of server-side languages for source code analysis alongside Java, Ruby, Perl and Python.
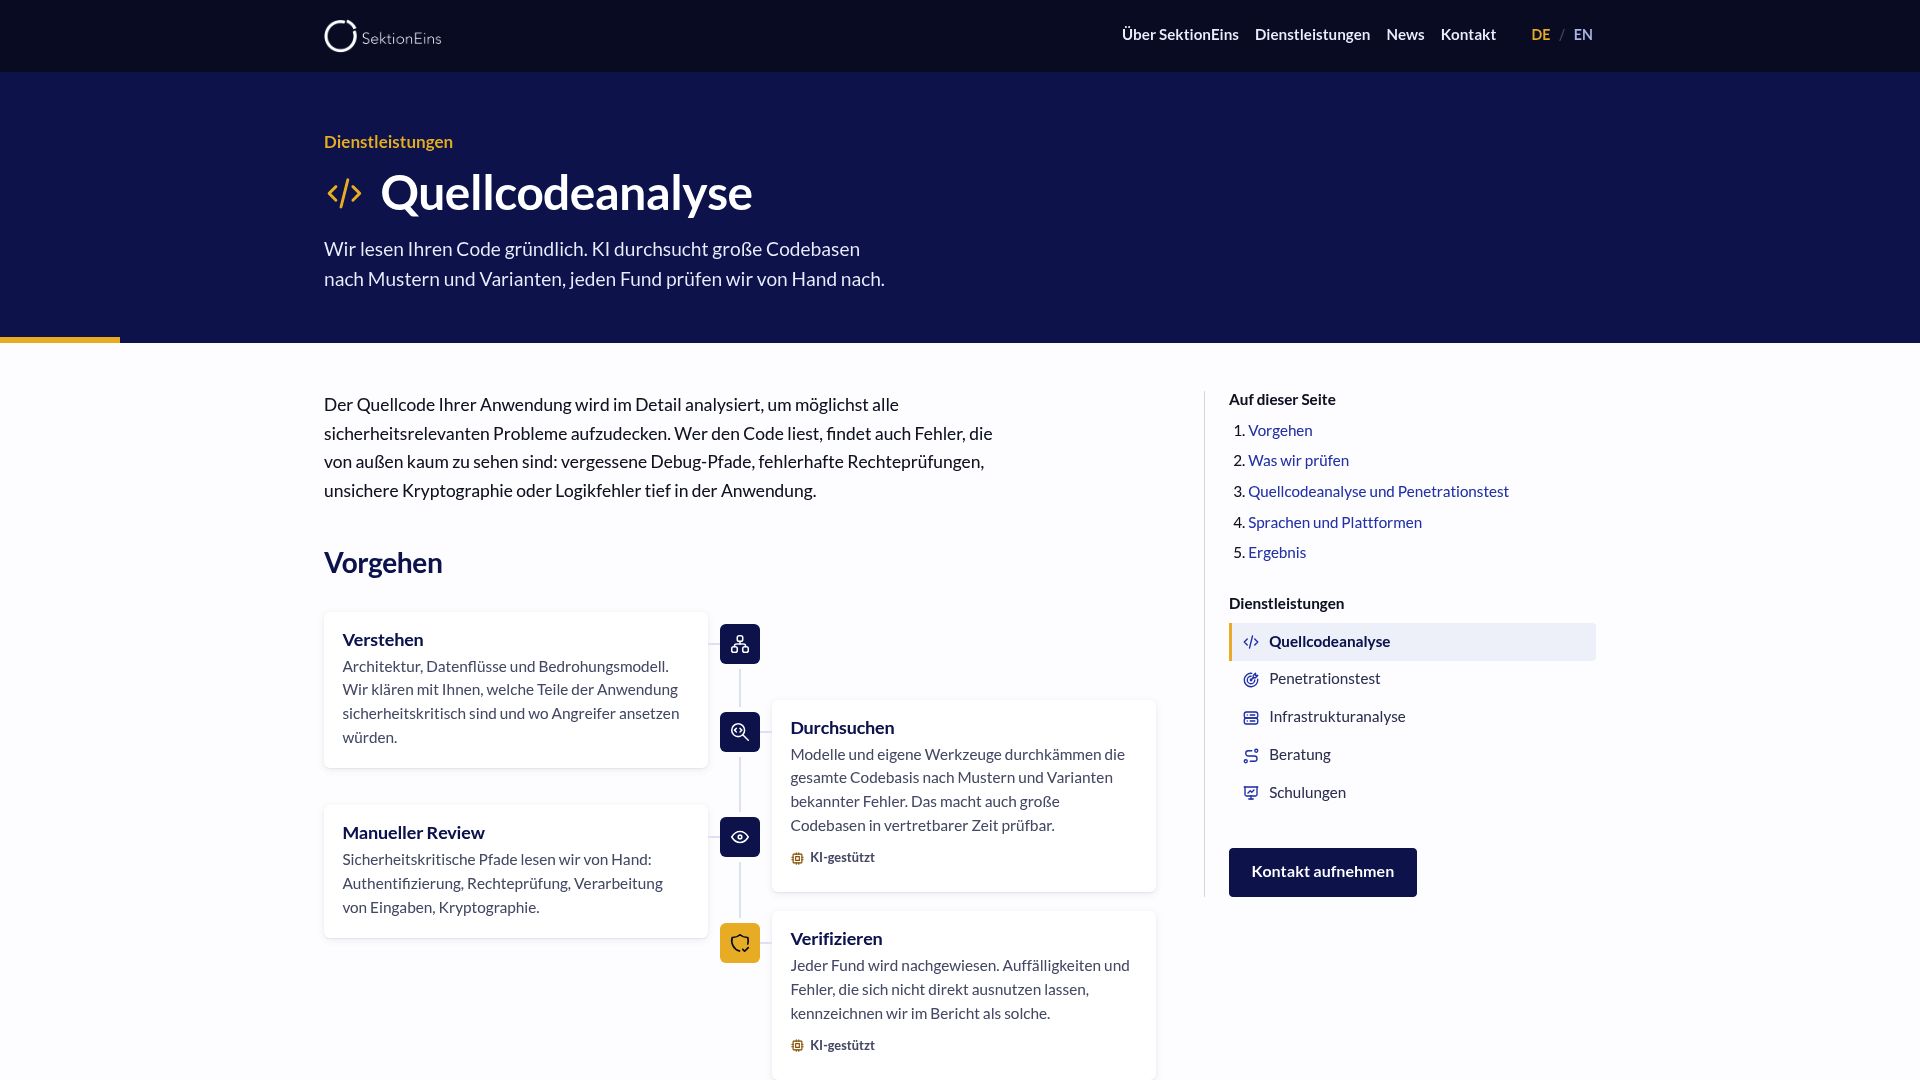
The source code analysis runs in four stages. The team first maps architecture, data flows and the threat model with you. AI models and the firm’s own tools then scan the whole codebase for known bug patterns and their variants. Experts read the critical paths by hand, including authentication, access control, input handling and cryptography. Finally, each finding is demonstrated, and issues that cannot be exploited directly are labeled as such. The work is structured around the OWASP Web Security Testing Guide and covers all OWASP Top 10 categories.
You can choose a short summary or a detailed report with a description, risk rating and remediation advice for each vulnerability, and follow-up questions are included. SektionEins usually recommends pairing code analysis with a penetration test to confirm findings on the running system.
Best for: European companies and large PHP codebases that want a methodical, OWASP-mapped review from a team with long PHP hardening experience.
Valorin Security is run by Stephen Rees-Carter, a Brisbane, Australia security consultant who specializes in security audits and pentesting for Laravel and PHP sites. He has been building and hacking Laravel apps since 2013, writes the Securing Laravel newsletter and gives conference talks on thinking like a hacker in Laravel.
A Laravel security audit with Valorin starts with a code review, and those findings guide a penetration test that runs against a staging or testing environment rather than production. Coverage includes authentication, authorization, third-party packages and the Composer supply chain, along with the kinds of issues automated scanners tend to miss. Clients choose between code-only coverage and code plus infrastructure.
One detail developers tend to appreciate: findings are shared as they are discovered instead of arriving all at once in a final report, and follow-up questions are answered after the audit. A review of your fixes can be arranged later, and lighter, smaller-scope security reviews are available for teams that do not need a full audit.
Best for: Laravel product teams that want a reviewer who knows the framework’s internals and package ecosystem in depth.
4. Patchstack — WordPress Plugin And Theme Code Audits
Patchstack is an Estonian company, registered in Pärnu, that runs a WordPress vulnerability database and sells paid security audits to plugin and theme developers. Its audits are manual code reviews by a security team that specializes in WordPress software, and they are not black box: Patchstack requires access to the source code, which you can share by email, repository invite or secure transfer link.
An audit is scoped by hours spent rather than by the number of vulnerabilities found, and each quote is based on code complexity, lines of code and number of files. The deliverable is a set of actionable results with guidance on how to patch each issue. Patchstack does not write the fixes for you, but it helps with patching if needed and offers post-audit support to confirm fixes. For publicly available software, it discloses findings only after they are resolved.
The same page lists SOC 2 and ISO 27001 certifications and a managed vulnerability disclosure program, which plugin vendors can use alongside an audit to prepare for the EU Cyber Resilience Act.
Best for: Commercial WordPress plugin and theme vendors that want a PHP code audit from a team that sees WordPress vulnerabilities every day.
5. Zend by Perforce — PHP Security Audit From The PHP Runtime Vendor
Zend, now part of Perforce Software with its contact address in Minneapolis, sells a dedicated PHP Security Audit alongside its architecture and performance audits. Its experts review your application and code to find attack vectors, exploits and PHP vulnerabilities, and the page names cross-site scripting, cross-site request forgery, SQL injection, remote code execution, denial of service and timing attacks among the issues covered. The audit also flags compliance issues.
An engagement starts with an interview, and Zend works from source code, configurations and safe snapshots or non-production environments, so no production changes are required. Findings are reported and discussed with you, and every audit includes clear, prioritized recommendations tied to business risk and effort. If you want help acting on them, Zend offers optional implementation services to harden the application.
Timelines are estimated during the interview phase, and pricing is by custom quote.
Best for: Enterprises running large or legacy PHP estates that want an audit from a PHP-focused vendor and may want hardening help afterward.
Software Secured is a Canadian application security firm whose secure code review service lists PHP among its supported languages, along with Python, Ruby, Java, C#, TypeScript and others. The method blends automated static analysis, manual inspection of critical modules and a 120-point checklist, with manual effort focused on authentication, authorization, cryptography and session handling. Experts validate findings to remove false positives.
Reports include prioritized issues with CVSS and DREAD scoring, business impact statements, reproduction steps and developer-ready remediation guidance, and findings can flow into Jira, Azure DevOps and Slack. Retesting can be requested within 12 months of report delivery and is scheduled within about two weeks of the request.
Software Secured is one of the few firms here that publishes a price: its secure code review starts at $9,300 USD on the Security Made Easy tier, with quotes based on lines of code, languages and business needs and delivered within 48 hours.
Best for: SaaS companies that want a predictable starting price, ticketing integrations and a long retest window.
MconnectMedia is a Magento and Adobe Commerce development company headquartered in Ahmedabad, India, with a delivery office in Kennesaw, Georgia. Its Magento security audit covers the Magento core, third-party extensions, custom code, infrastructure, admin access, payment flow and database. The custom code review targets SQL injection, XSS, CSRF, authentication bypass and path traversal in your /app/code modules, while the extension review looks for known CVEs, unmaintained packages and dependency confusion.
The audit combines manual code review, automated scans and an infrastructure check, with a senior reviewer cross-checking every critical and high finding. An NDA is signed before kickoff, the team works with read-only access and does not write to production during an audit. The page credits the work to Adobe-certified Magento security analysts with more than 240 audits behind them.
Pricing and timing are published. The headline audit has a 5-day turnaround and produces a 30 to 50 page report with a prioritized remediation roadmap, where each finding carries a CVE reference, severity, reproduction step and recommended fix. A Quick Scan starts from $1.8k fixed and takes 2 days, and an Audit plus Pen-test plus Fixes package starts from $9.8k fixed over 2 weeks, including a retest.
Best for: Magento and Adobe Commerce merchants who want a fixed price and fast turnaround on a store and extension review.
Websec is a security consultancy headquartered in Victoria and Vancouver, British Columbia, offering application security, network security, adversary simulation and risk work. Its secure code review covers PHP along with Java, JavaScript and TypeScript, C#, Python, Ruby, Go and more.
The review runs in four stages: scoping and planning, automated static analysis, expert manual review and then reporting and remediation. Websec describes the approach as manual-first. The manual work concentrates on business logic and architectural flaws, cryptographic implementation and authentication and authorization controls, which are the areas automated tools tend to miss in PHP applications.
You receive prioritized findings with CVSS scores and code-level remediation recommendations with examples, plus follow-up support and optional fix verification. Websec also runs secure development and DevSecOps training for teams that want to carry the lessons into their workflow.
Best for: Teams whose biggest risks sit in business logic and access control rather than in the obvious injection bugs.
Securing is a Kraków, Poland security testing firm that has been testing since 2003. Its security code review is a white-box service, and PHP is on its list of languages, alongside C#, Java, Python, Golang, JavaScript, Swift and others. The firm also takes requests for less common technologies.
Every review has an automated part and a manual part. Tools cover large volumes of code quickly, and a human analyst then works through the results to judge context and real risk. Securing positions the review as a complement to penetration testing, which suits PHP teams that want both a code-level view and confirmation of what is exploitable in the running app.
Quotes are custom. You answer a short set of questions so Securing can estimate the workload and the skills required, and it may follow up before making an offer. The team reports CVEs and speaks at international security conferences.
Best for: European companies that want a secure code review and a penetration test from the same team.
Cure53 is a Berlin security firm founded in 2007 that brings together independent security experts on a project basis. Alongside classic black-box penetration tests, it offers white-box tests and code audits, and it names PHP among the languages its team works with, together with JavaScript, Java, Ruby, Python and Perl.
What sets Cure53 apart is transparency. It publishes reports when the project maintainers or the sponsor of the test request it, and its public archive includes a test of the PHP library php-saml-sp and several reviews of the Passbolt backend and plugins. That gives buyers a way to read real Cure53 deliverables before they sign. During engagements the team prefers direct contact with developers so bugs and fixes can be discussed as they are found.
Best for: Open source projects and high-scrutiny PHP applications that want a public, citable audit report.
How To Choose A PHP Security Audit Company
Does The Firm Name PHP And Your Framework In Its Code Review Offering?
A secure code review is only as good as the reviewer’s knowledge of your stack. Laravel’s mass assignment and Blade escaping, Symfony’s security voters, WordPress nonces and capability checks and Magento’s module structure each have their own failure modes. Look for a firm whose service page lists PHP, and ideally your framework, and ask who on the team has reviewed that framework before. If you are still choosing a build partner, our lists of top PHP development companies and Laravel development companies are a good starting point.
How Much Of The Review Is Manual?
Static analysis tools are fast, but they miss broken access control, business logic flaws and insecure deserialization paths that only make sense in context. Ask what share of the engagement is manual reading of code, which paths get line-by-line attention, and how the firm removes false positives before you see the report.
What Exactly Will You Receive?
Ask for a sample report. A useful PHP code audit report names the file and line, explains the impact in plain terms, rates severity with a standard like CVSS, and gives a fix your developers can apply. Some firms go further and send patches or pull requests. Our guide to what belongs in a penetration testing report applies to code audit reports too.
Is Fix Verification Included?
Findings only matter once they are fixed. Check whether a retest or fix review is included in the price, how long the window lasts and whether you get an updated report you can show customers or auditors.
Do You Need A Code Audit, A Pentest Or Both?
A code audit finds flaws at the source, including ones that are hard to reach from outside. A penetration test confirms what an attacker can actually exploit in the running app and its infrastructure. Several firms here recommend combining the two. Ask each firm whether it can do both, or budget for a separate test.
Frequently Asked Questions
What Does A PHP Security Audit Cover?
A PHP security audit reviews your source code, and often your configuration and dependencies, for flaws such as SQL injection, cross-site scripting, cross-site request forgery, file inclusion, PHP object injection, broken authentication and access control, weak cryptography and insecure password storage. Good audits also check third-party packages and the Composer supply chain, and for platforms like WordPress or Magento, the plugins, themes and extensions you have installed.
How Much Does A PHP Security Audit Cost?
Most firms quote per project based on lines of code, number of files, frameworks and how much of the app is in scope. Few publish prices. Of the firms above, Software Secured lists its secure code review as starting at $9,300 USD, and MconnectMedia lists a Magento Quick Scan from $1.8k fixed and an audit, pentest and fixes package from $9.8k fixed. Everyone else quotes after a scoping call.
How Long Does A PHP Code Audit Take?
It depends on codebase size and scope. A focused review of one plugin or module can be quick, while a large custom platform takes longer. MconnectMedia publishes a 2-day Quick Scan and a 5-day standard Magento audit, while firms like Zend and Paragon Initiative Enterprises agree on a timeline during scoping. Plan for scheduling lead time and a retest after your fixes as well.
What Is The Difference Between A PHP Security Audit And A Penetration Test?
A PHP security audit, or secure code review, is white-box work: the reviewer reads your code to find flaws at the source. A penetration test attacks the running application, usually with little or no code access, to prove what is exploitable. Code review tends to be more thorough on logic and hidden paths, while pentesting confirms real-world impact and catches server and configuration issues.
Conclusion
The Top PHP Security Audit Companies In 2027 range from PHP specialists like Paragon Initiative Enterprises, SektionEins and Valorin Security to platform-focused auditors for WordPress and Magento and broader application security firms that include PHP in their secure code review. Start with the firm whose service page matches your framework, ask for a sample report and confirm that fix verification is part of the deal.
If you want to feature your company on this list, email us or submit a form in the Top Choices section. After a thorough assessment, we’ll decide whether it’s a valuable addition.